Agent + MCP Discovery
Discover real agents, MCP servers, models and tools from authorized connected sources.
ELITZE connects discovery, identity, reachability, policy enforcement, authorized execution, runtime validation and evidence around the actions AI systems actually take.
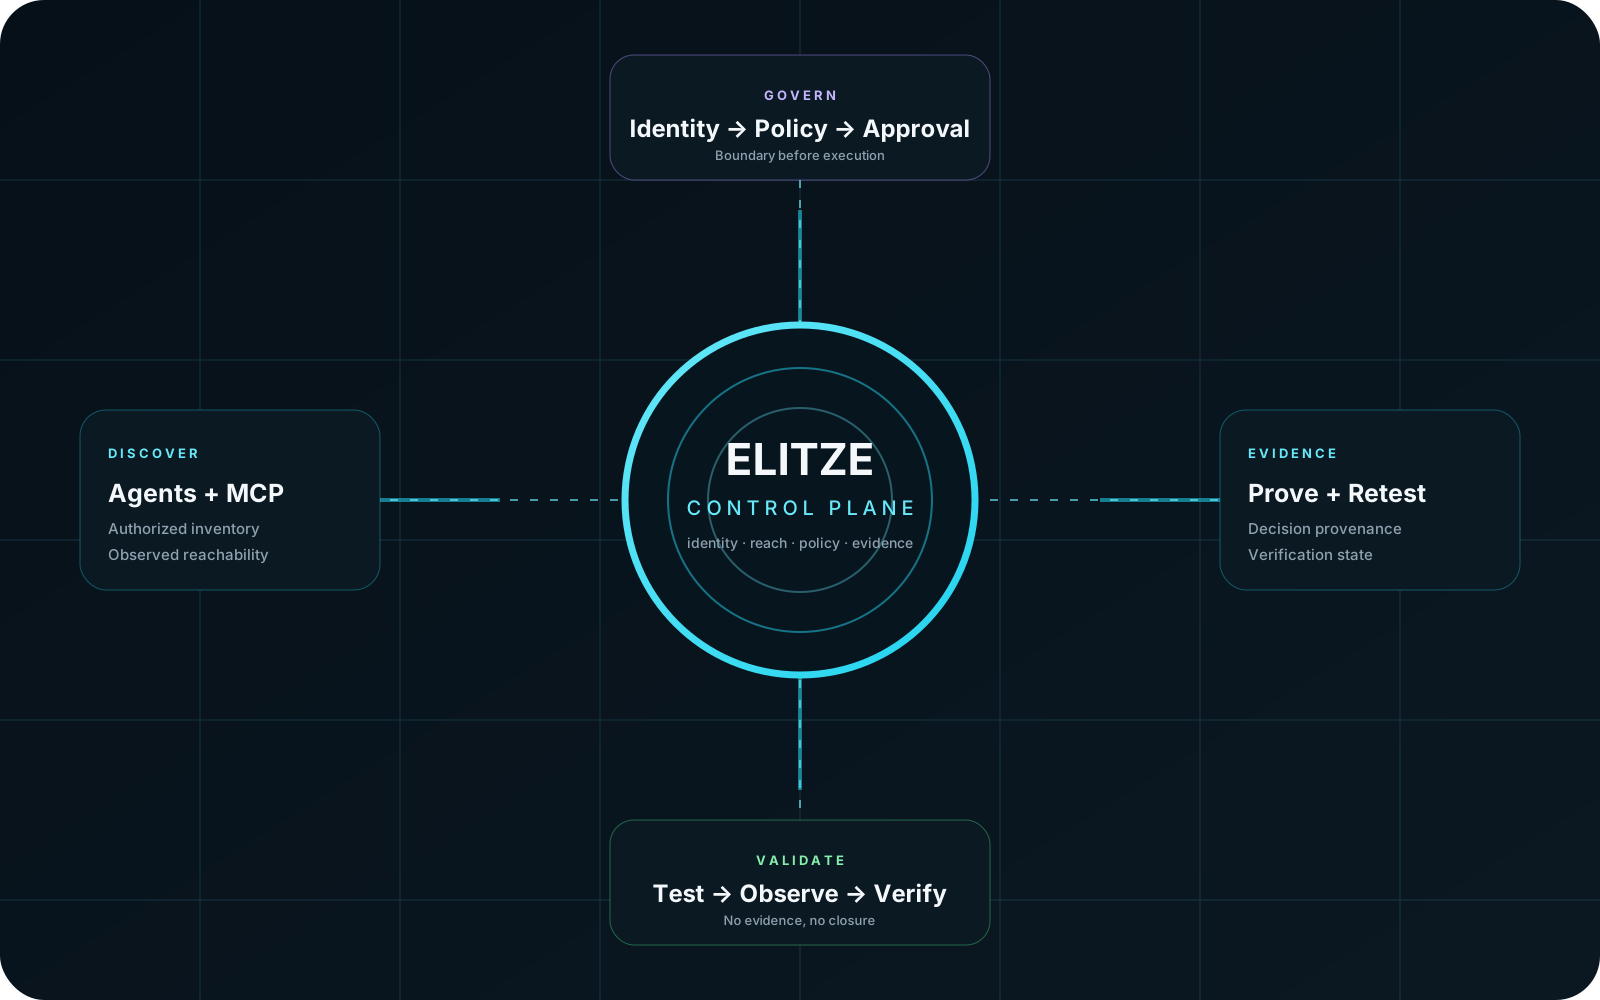
Discover real agents, MCP servers, models and tools from authorized connected sources.
Bind agents, MCP servers and tools to tenant-scoped workload identities.
Map observed identity-to-tool, API, secret and data relationships without inventing reach.
Evaluate sensitive actions before execution with explicit decisions.
Separate policy evaluation from execution at the authorized boundary.
Preserve decision evidence, observe the actual result and retest before closure.
Track observed paths from workload identities to protected data and secrets.
Capture actual runtime outcomes instead of presenting dashboard state as evidence.
No mock records, fake telemetry, synthetic metrics, simulated events or invented outcomes.
Discovery, identity, reachability, policy, authorized execution, runtime observation, adversarial validation, retest and evidence stay connected.
Sensitive actions stay bound to a tenant-scoped subject identity.
Sensitive tool and MCP actions cross policy before the execution boundary.
A status change is not proof; the affected path must be observed and retested.
Authorized pentest requests, red-team release testing, attack-path validation and evidence integrity are represented in the security skill registry. Actual test completion remains evidence-gated.
Open validation workbench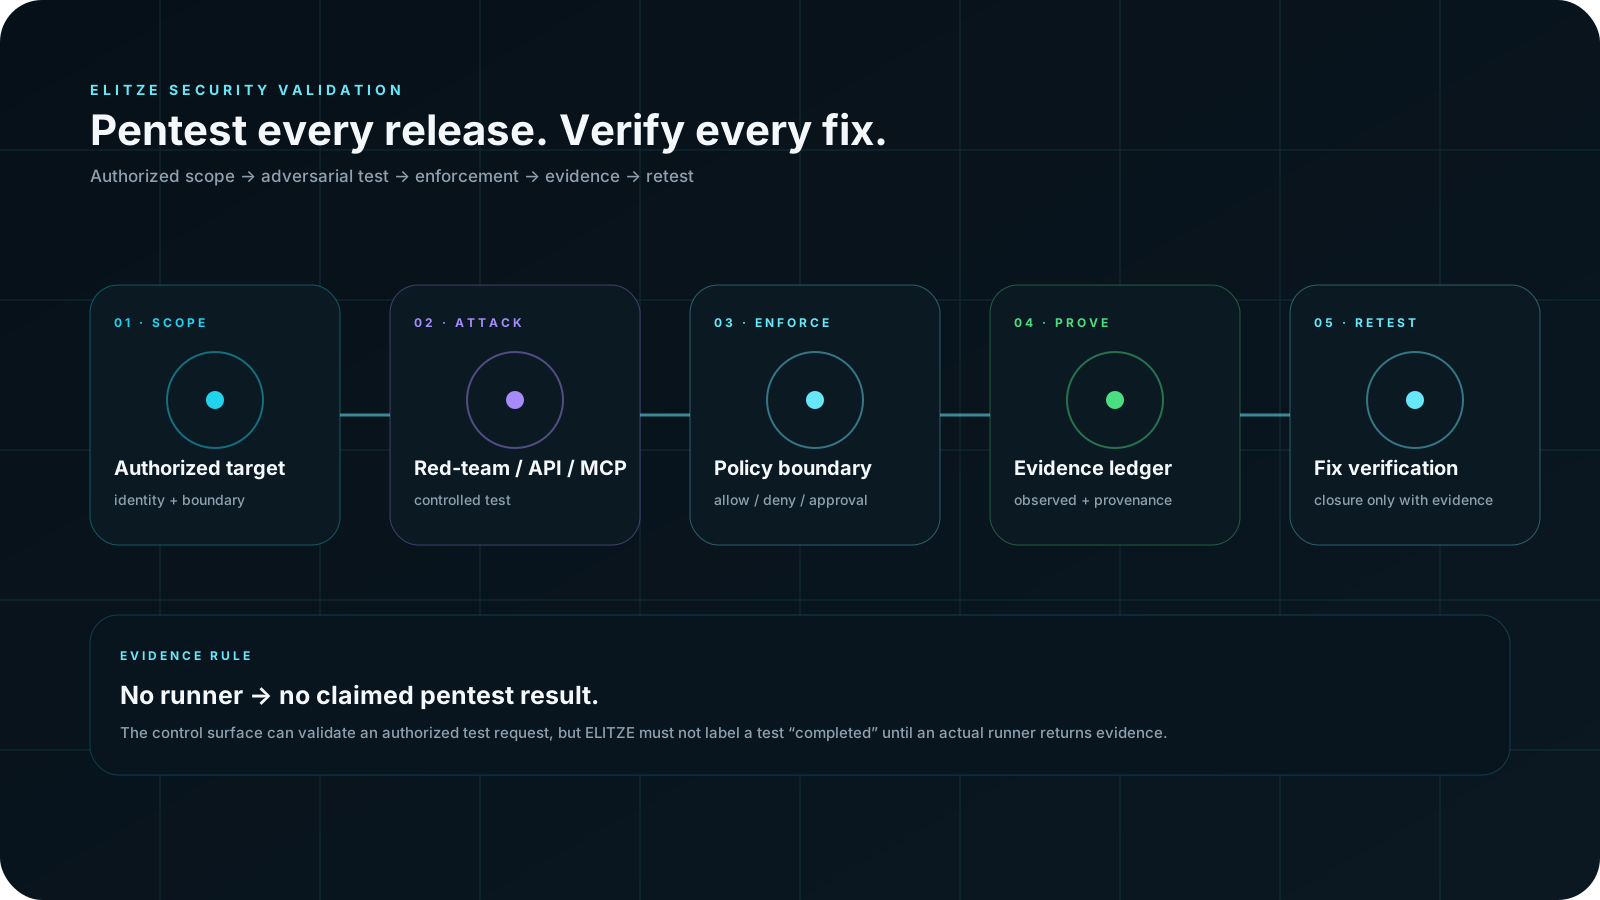
Connected integrations must supply the records behind inventory, decisions, runtime outcomes and verification.